
Can SOC SIEM Consulting Fix the Visibility Gaps in ICT Security?
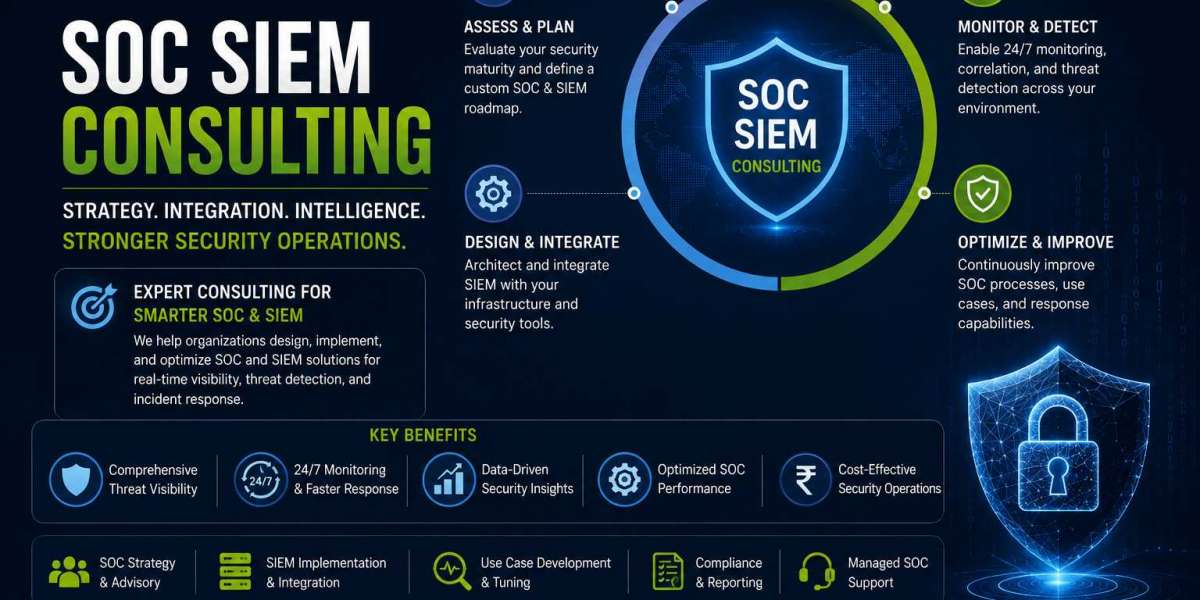
ICT companies increasingly depend on interconnected networks, applications, cloud environments, endpoints, and digital communication systems. That connectivity creates valuable operational visibility, but it also produces a large volume of security information. soc siem consulting can help Indian ICT businesses make that information more useful by improving how security events are collected, interpreted, prioritized, and incorporated into security operations.
The objective is not simply to add another cybersecurity layer. It is to create a monitoring approach that helps security teams understand what is happening across their technology environment and determine what deserves attention.
What SOC SIEM Consulting Can Improve
SOC SIEM consulting brings together Security Information and Event Management capabilities with security operations processes. It can be used to assess an existing SIEM environment, identify monitoring gaps, improve event visibility, and establish more effective processes for handling security alerts.
For an ICT business, this matters because security information often comes from many different technologies. Without a clear strategy, an organization can collect substantial amounts of data while still struggling to identify meaningful security activity.
Consulting helps connect the technical configuration of a SIEM with the practical requirements of security operations.
How SOC Services Companies in India Fit Into the Picture
Indian ICT organizations considering soc services companies in india should look at how a potential service arrangement addresses both technology and operations.
A SOC service may provide monitoring and analysis, but its effectiveness depends on whether the underlying security information is relevant, accessible, and appropriately prioritized.
For this reason, an organization should evaluate how security events move from collection to analysis and eventually to escalation. The process should be understandable to both technical teams and business stakeholders.
The right arrangement can help an ICT company strengthen its security operation without treating SIEM as an isolated software implementation.
The Problem With Alert Accumulation
A SIEM can centralize large amounts of security information. However, more information does not automatically produce better security.
Poorly tuned monitoring can generate repetitive alerts, low-value notifications, or events that lack enough context to support investigation. Analysts may then spend time reviewing activity that does not represent meaningful risk.
Over time, alert fatigue can affect the effectiveness of security operations.
An organization may respond by reducing the number of alerts, but indiscriminately suppressing events can create another problem. The better approach is to understand why alerts are being generated and determine which signals actually support security decisions.
SIEM Optimization Requires Context
A useful SIEM strategy begins with understanding the business and technical environment.
ICT organizations should know which systems are critical, which activities are expected, which events deserve additional scrutiny, and which security signals can help analysts investigate suspicious behavior.
This context allows monitoring rules and workflows to be designed around actual operational requirements rather than generic assumptions.
soc services companies in india can play a useful role when their security operations are aligned with these requirements and when responsibilities between the provider and customer are clearly defined.
A Practical Framework for SIEM Evaluation
Before changing an existing SIEM environment or engaging a managed security operation, ICT decision-makers should examine several areas.
Area | What to evaluate |
Data sources | Are relevant systems generating security information for analysis? |
Data quality | Is the collected information useful and appropriately structured? |
Alert volume | Are analysts receiving excessive low-value notifications? |
Correlation | Can related events be examined as part of a broader activity pattern? |
Detection logic | Do monitoring rules reflect the organization's environment? |
Investigation | Is there a clear process for examining important alerts? |
Escalation | Are responsibilities defined when an incident requires action? |
Reporting | Can security findings be communicated in a useful way? |
Continuous improvement | Are monitoring rules reviewed as the environment changes? |
This framework helps organizations evaluate whether their SIEM is supporting security operations or simply storing security events.
What Better SIEM Operations Can Deliver
One of the most important benefits is improved visibility. Relevant events can be brought together in a way that makes investigation more practical.
Better alert prioritization can also help analysts concentrate on activity that requires attention. Reducing unnecessary noise can make security operations more manageable without relying on blanket suppression.
A structured approach can further improve consistency. When investigation and escalation procedures are defined, security teams have a clearer method for handling suspicious events.
For ICT companies, these improvements can support operational resilience as technology environments become more distributed and interconnected.
An ICT Scenario: Connecting Separate Security Signals
Imagine an ICT organization operating several interconnected services. An unusual authentication event occurs at approximately the same time as unexpected activity on an endpoint.
Individually, the events may not provide enough information to determine whether there is a genuine security concern.
A properly designed SIEM process can bring related events into a common analytical view. Security personnel can then examine the surrounding context and determine whether the activity warrants investigation or escalation.
The important point is not that every correlated event represents an attack. Correlation provides additional context that can help analysts make more informed decisions.
A Practical SIEM Improvement Checklist
ICT organizations can strengthen their SIEM strategy by reviewing the fundamentals regularly.
- Identify the systems that generate the most valuable security information.
- Remove unnecessary data sources that provide little security value.
- Define the purpose of each important detection rule.
- Review recurring alerts for false positives and avoidable noise.
- Establish priorities for different categories of security events.
- Document investigation and escalation procedures.
- Keep ownership clear between internal teams and external security operations.
- Update monitoring logic when applications or infrastructure change.
- Review security reports for recurring patterns.
- Periodically assess whether the SIEM continues to support business priorities.
These actions help ensure that SIEM remains an operational security capability rather than a static technology deployment.
Governance and Compliance Considerations
ICT businesses may have obligations related to information security, privacy, customer contracts, internal policies, and applicable regulatory requirements.
Security event monitoring can support some governance activities by creating greater visibility into relevant activity. However, the presence of a SIEM or SOC service does not itself establish compliance.
Organizations should determine which obligations apply to their specific operations and design security monitoring, logging, retention, reporting, and incident processes accordingly.
A managed or consulting relationship should complement those internal governance requirements rather than replace them.
Creating a More Useful Security Operation
The real measure of SIEM maturity is not the quantity of data collected. It is whether security personnel can use that information to identify meaningful activity and make better decisions.
For Indian ICT organizations, soc siem consulting can help close the gap between security technology and security operations by examining data sources, detection logic, alert quality, investigation processes, and escalation workflows.
When SIEM is designed around the organization's actual technology environment and business priorities, security teams can spend less effort navigating unnecessary noise and more effort understanding events that genuinely deserve attention. That makes the monitoring function more practical, adaptable, and valuable over time.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com